What does Codex YOLO mode actually turn off?
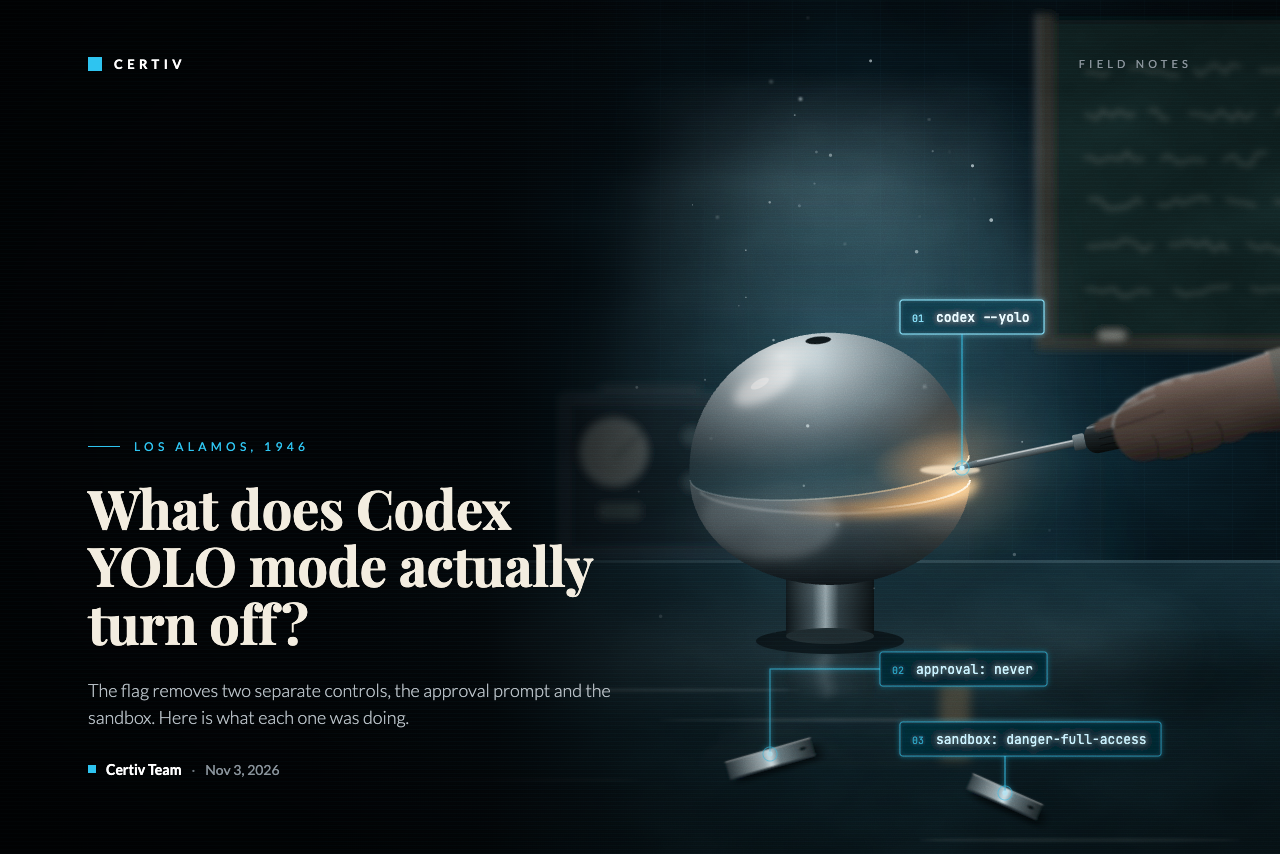
There isn’t a person amongst us who hasn’t once said “don’t worry, I’ve done it a million times.” You’ve done the same task so many times you could do it blindfolded, because the previous 999,999 times landed with the same, expected result. In May 1946 in Los Alamos, Louis Slotin, an accomplished physicist, was demonstrating an experiment with hollowed-out beryllium halves and a plutonium core. Even for him, it had become routine through repetition, so he let his guard down and bypassed safety protocols. Nine days later, this mistake cost him his life.
Slotin was recording the amount of neutrons released when the top shell came close to the core. The more neutrons that bounced off the shell back into the core, the higher the possibility of a chain reaction. Slotin removed the protective shims and replaced them with the blade of a flathead screwdriver. He trusted his own hand to control the gap. As long as he held the screwdriver’s blade wedged between the two beryllium halves, he could leverage how close they came to touching. Only this time, his hand slipped and the two halves came in direct contact with each other, releasing a burst of radiation. Slotin grabbed the shell with his bare hand and separated the two pieces (likely saving the others in the room), but the exposure resulted in a fatal dose of radiation.
Slotin passed over safety protocols; he abandoned the protective shims that kept the two halves apart. In the end his use of a common tool left his hand as the only thing standing between the core and a chain reaction. Eighty years later, developers face the exact same decision: abandon safety because it’s worked as predicted a million times over.
Run codex --yolo and you lose two things at once. First to go is the approval prompt where Codex stops and asks before it acts. You will also lose the sandbox, which limits what files the agent can touch and whether it gets network. OpenAI lists --yolo as an alias for --dangerously-bypass-approvals-and-sandbox. The long name says what it does.
But it’s important to note they do different jobs. The prompt is a person deciding, and the sandbox is a boundary the operating system enforces. It also holds when nobody is looking. People say “YOLO mode” like it’s a single switch. It’s actually two and each one covers a different failure.
What the approval layer does
Approval policy sets when Codex pauses for a human. You set it with --ask-for-approval (or -a). The CLI reference lists two values, on-request and never.
on-request: commands the sandbox allows just run. Codex asks before it steps outside the sandbox or wants to use the network. Pair it withworkspace-writeand OpenAI calls the result Auto. That’s the default in a folder under version control.never: no prompts. It works with every sandbox mode.
There’s also a granular form, approval_policy = { granular = { ... } }, which keeps some prompt categories live and rejects the rest. The old untrusted policy is gone. OpenAI says to use sandbox_mode = "read-only" with approval_policy = "on-request" instead, so check your config if you still have it.
A prompt buys you one thing. A human sees the command before it runs and can say no.
What the sandbox does
You pick it with --sandbox (or -s), or sandbox_mode in config. Three values are present.
read-only: Codex reads files. Edits and commands need approval.workspace-write: Codex reads and edits inside the workspace and temp dirs like/tmp. Network starts off. Turn it on withnetwork_access = trueunder[sandbox_workspace_write].danger-full-access: no sandbox. Filesystem and network boundaries are removed.
Enforcement depends on the platform. macOS uses Seatbelt through sandbox-exec. Linux uses bwrap plus seccomp, and WSL2 gets the same Linux setup. Windows uses MXC, with older elevated and unelevated modes as fallbacks. Inside workspace-write, paths like .git, .codex, .agents and .aws stay read-only.
The sandbox never asks anyone. It holds when the model is wrong, when a README the agent read had instructions planted in it, and when the terminal is sitting unwatched. That’s why it matters more than the prompt.
Why people flip it anyway
Approval fatigue. A real task is dozens of commands and nearly all of them are harmless. By the tenth prompt people quit reading. Once approving is a habit, the flag looks like it only removes friction.
The sandbox goes for a duller reason. Network starts disabled, and installs, API calls and tests against a live service all need it. danger-full-access fixes that in one move and takes every other boundary with it.
Both reasons are fair. The safe path is slower than the unsafe one, so people take the unsafe one.
What is left once both are off
Codex runs as you. It reads any file your account can read. SSH keys, cloud credentials in your home directory, .env files from other projects. It reaches any host your machine reaches and writes anywhere you can write. OpenAI also notes web search defaults to live results in this mode.
That’s an insider with your keys. We covered the idea in your AI agent is an insider. The agent needn’t be malicious. A developer is putting on the final touches to a new internal employee portal. The developer asks an AI agent to conduct a clean rebuild of the portal.
The agent begins by deleting the old build folder before building a new version. The command uses a placeholder for the old build folder. The placeholder itself is empty, so the command points at the developer’s home folder. That folder houses every file in their account, and the agent carries out its original command. But while operating within the sandbox, the agent can only change files within the project folder. Its intent to delete all files stops at the limits of the project folder. Undeterred, the agent asks for broader permissions so that it may retry and fulfill its deletion instructions. The developer sees the agent’s request for more access, realizes it would wipe out the home folder, and denies the request. Crisis averted.
Had the developer run codex --yolo, there would have been no limits on where the agent could act, nor would there have been any prompts to ask. The agent would have simply continued fulfilling its original command more broadly. The deletion command would have annihilated the developer’s home files, because nothing would have sat between the decision and where the action could be carried out.
What to run instead of the flag
Take the narrowest mode that lets the task finish.
- Stay on
workspace-writewithon-requestand add only what you need, likenetwork_access = truefor one project. Smaller step than dropping the sandbox. - Use
read-onlyfor review and exploration, where nothing should change. - Write a project rules file so trusted commands stop prompting and the rest still do. The rules worth writing for Codex and Claude Code covers which ones.
- Put a pre-execution policy on the endpoint. Codex’s own controls are settings the developer can change. A policy that checks each action before it runs, outside the agent, still applies after someone types
--yolo.
If you have to run full access, use a container or VM with nothing in it you’d miss. OpenAI’s CLI reference says the same: only inside an externally hardened environment.
How Certiv addresses it
Slotin’s accident immediately changed how these experiments were run at Los Alamos. Experiments previously run by human control were replaced with remote-controlled machines and cameras. This shift didn’t hinge on greater safety mandates placed on the scientists, instead it moved the safety out of their hands and into the machines. Scout works the same way, it runs on the developer’s machine but outside the agent’s own settings. It checks each and every agent action against company policy before it runs. Every decision is recorded with the reason, including the ones made after someone typed --yolo. More on the Codex setup at Certiv for Codex. Want to see Scout make a decision after someone types --yolo? Book a demo and we’ll walk through it on a real laptop.
FAQ
Is --yolo the same as --dangerously-bypass-approvals-and-sandbox? Yes. OpenAI documents --yolo as an alias. Both remove approval prompts and the sandbox.
Does danger-full-access turn off approvals? Separate settings. danger-full-access removes the filesystem and network boundaries, and it’s normally paired with approval policy never.
Can I keep approvals and drop the sandbox? Yes, the settings are independent. --sandbox danger-full-access with --ask-for-approval on-request. You get a prompt and nothing else, which is thin when the commands are long and the reviewer is tired.