AI Agent Assurance capabilities
See each agent. Decide each action. Prove what happened.
Scout sees each agent. Sage judges each step against company policy before it runs.
Agent Discovery
Know what AI runs on each device.
Scout names each agent and the model it calls, with no SDK and no change to the agent.
- Agent discovery → Finds the AI agents on each device, including agents your team has not sanctioned and agents with no hooks, and ties each model connection to the app that made it.
- Endpoint inventory → For each device: its agents, MCP servers, and sessions.
- MCP servers Lists the MCP servers configured for Claude Code and Claude Desktop. Their secrets stay on the device.
- Models in use Which models are in use, the tokens each one uses, and the account it signs in with.
- Process and privilege context Records which app made each request, the user it runs as, and its privilege level.
- Tools and skills The tools and skills each agent used.
- Local models The models in LM Studio and Ollama on each device.
Pre-Execution Control
Each action gets a response before it runs.
Scout intercepts each action a supported agent proposes, on the machine and outside the agent, and Certiv answers with one of five responses before it runs.
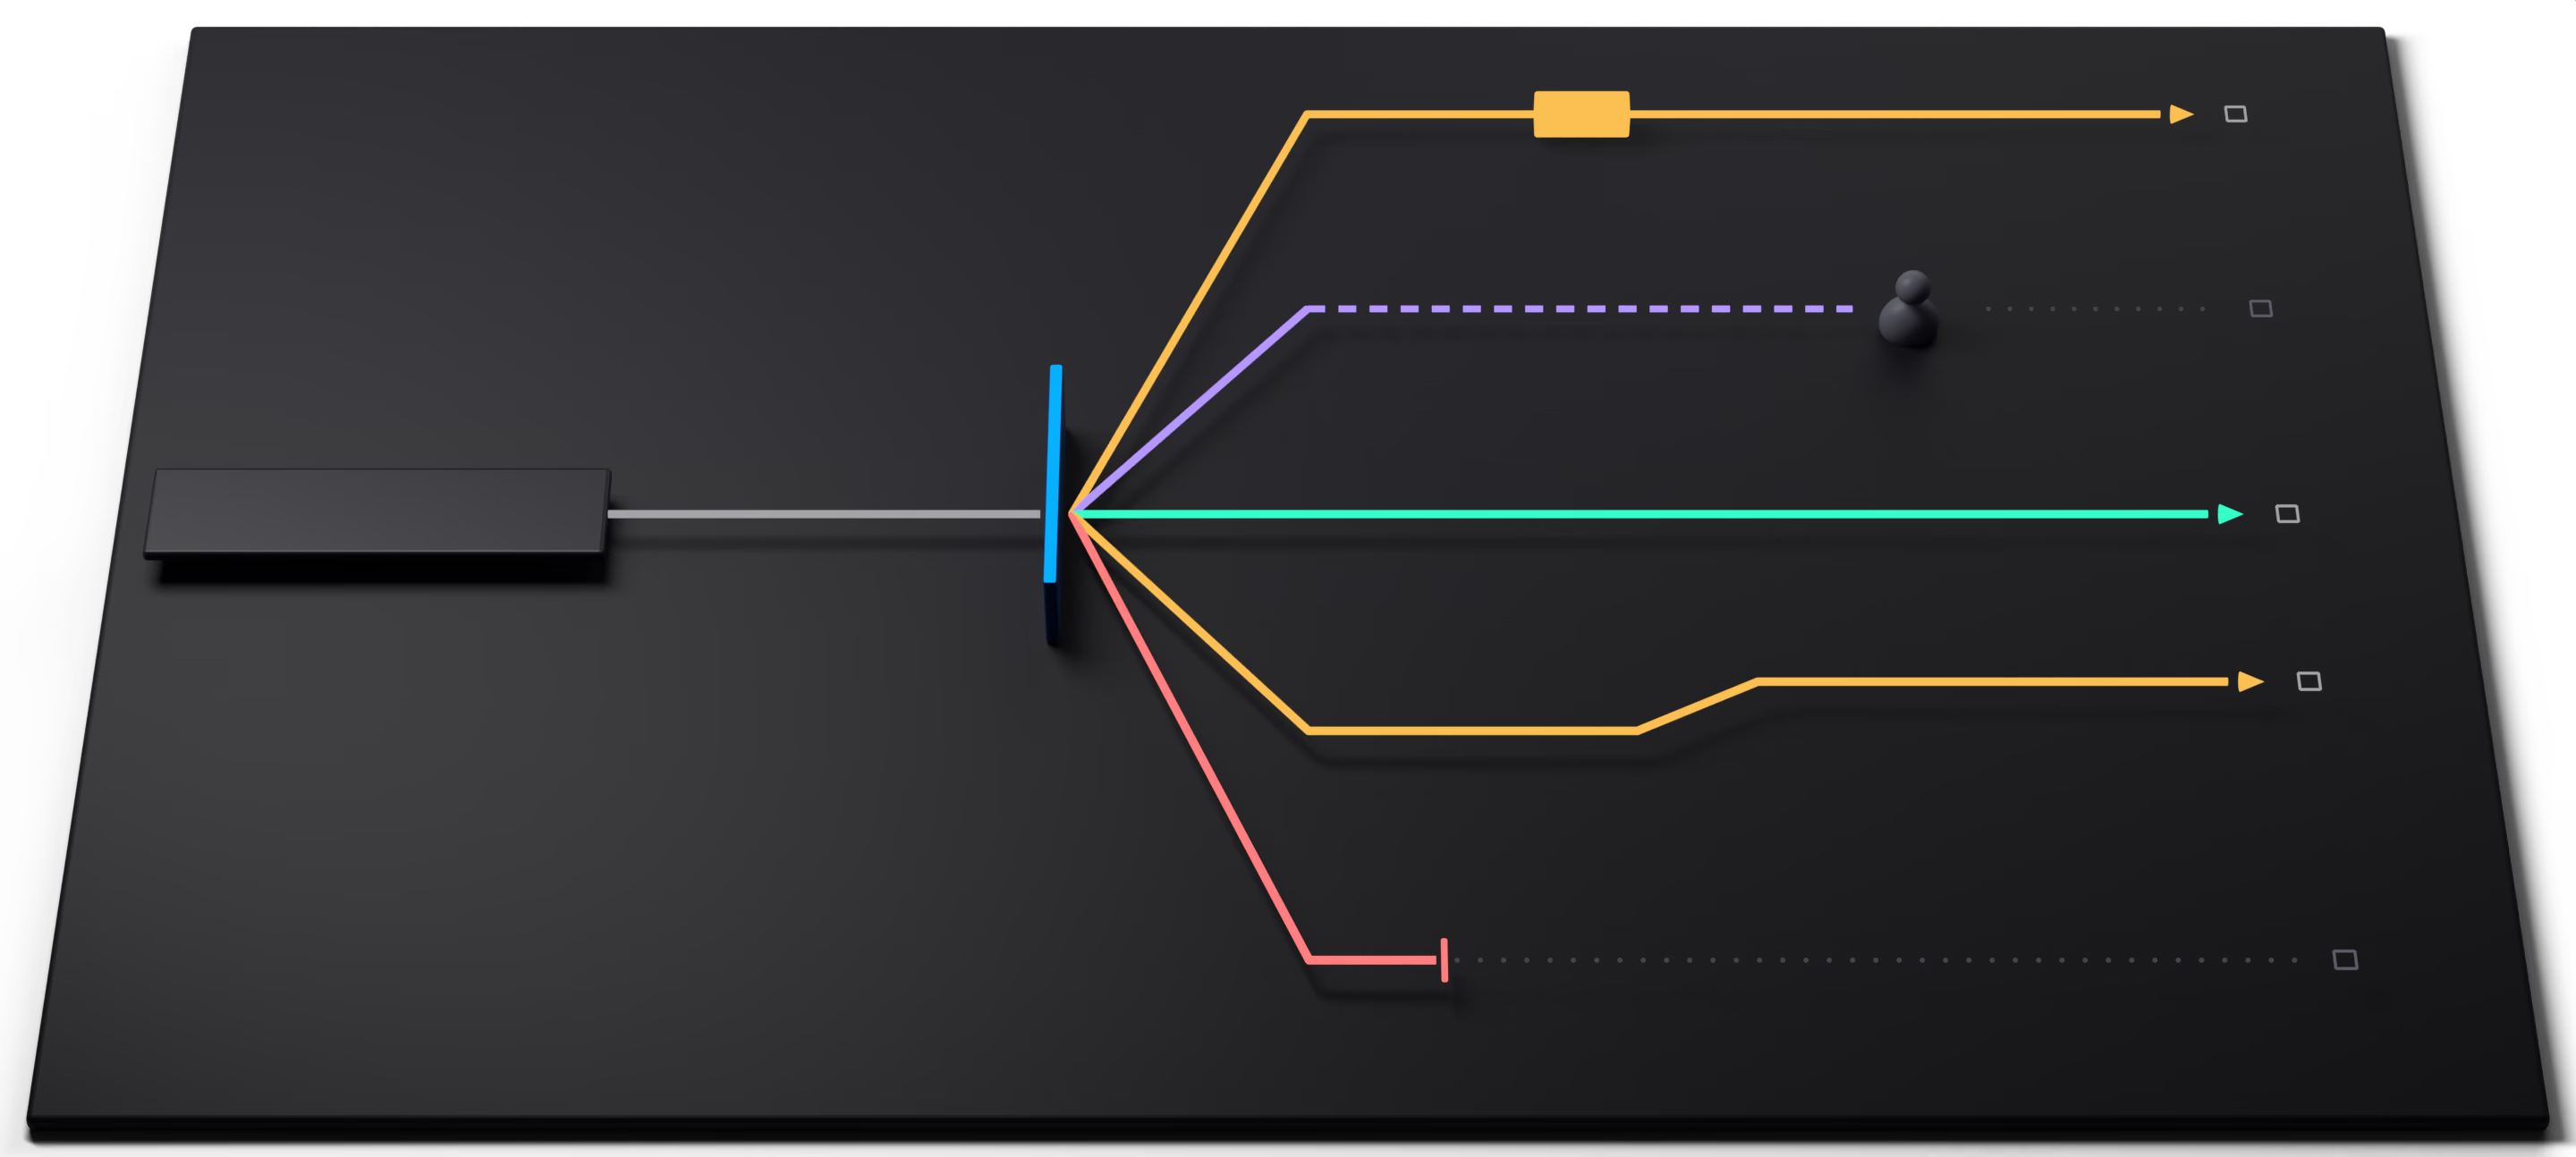 Claude Code
curl -X POST "$TEAM_WEBHOOK"
--data @build.log
One company policy
Redact
Runs without the key
Pause
Waits for approval
Allow and record
Runs, on the record
Steer
Takes a new path
Block
Does not run
THIS LAPTOP
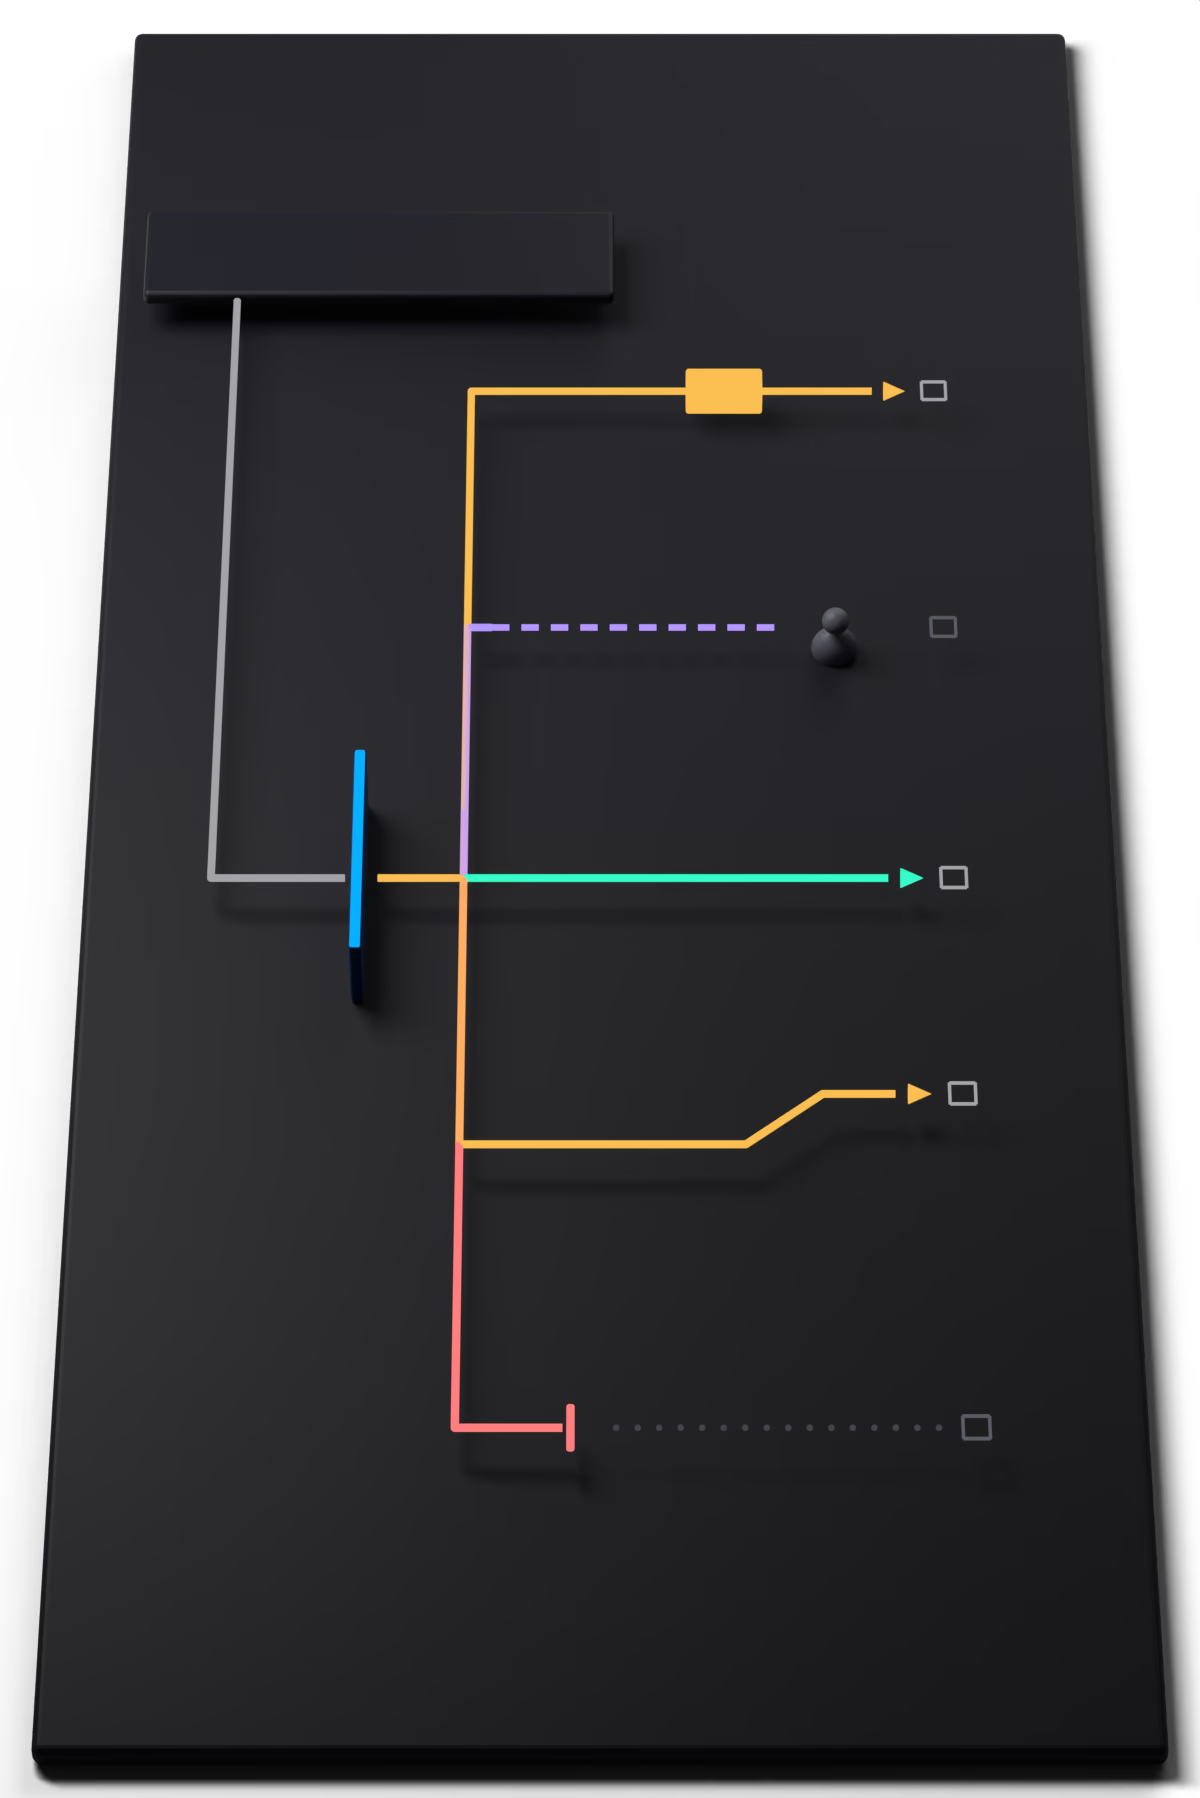 curl -X POST
"$TEAM_WEBHOOK"
--data @build.log
Claude Code
One company
policy
Redact
Runs without the key
Pause
Waits for approval
Allow and record
Runs, on the record
Steer
Takes a new path
Block
Does not run
THIS LAPTOP
- Pre-execution enforcement → Checks each action an agent proposes before it runs.
- On the machine, outside the agent Scout intercepts each action on the device, outside the agent, under company authority.
- Independent of provider and vendor Sits outside the model provider and the agent vendor, so it does not depend on either.
- Redact → Removes a matched secret from a request that can be rewritten, and lets the rest go on.
- Pause Holds the action for approval on the device. No answer before the timeout denies it.
- Allow and record Lets the action run and keeps the record.
- Steer Stops the call and tells the agent why, so it takes a different approach.
- Block Stops the action, so it does not run.
- Steer and continue Withholds the blocked step and lets the agent continue with the rest of the work.
- Fail-closed mode Blocks traffic Scout cannot attribute to an app.
Context and Judgment
Each step is judged in context.
Sage takes each proposed action apart, reads it against the task and the recent steps in the session, and runs every rule before one verdict is composed.
- Each action taken apart Classifies each argument of a tool call, parses shell commands, and reads nested calls.
- Judged with the task Reads the user’s last message and the last 15 tool calls with their verdicts.
- Deterministic and semantic checks Deterministic checks match the shape of a command. Semantic checks read what the call means.
- Strictest verdict wins Every rule runs, and the strictest response wins.
- Repeated Steers escalate A run of Steers in one session can escalate.
- Continuous authorization → Authorizes each action as it happens, with recent steps in the session.
- Declared intent → A declared intent becomes a rule that pauses a session that drifts from the task.
- Tools with no schema A tool Certiv has no schema for is still evaluated.
Company Policy
Write the policy once. Tune it by group.
Company policy applies to each supported agent and model. Test it on a recorded session, run it in audit first, and tune it by group.
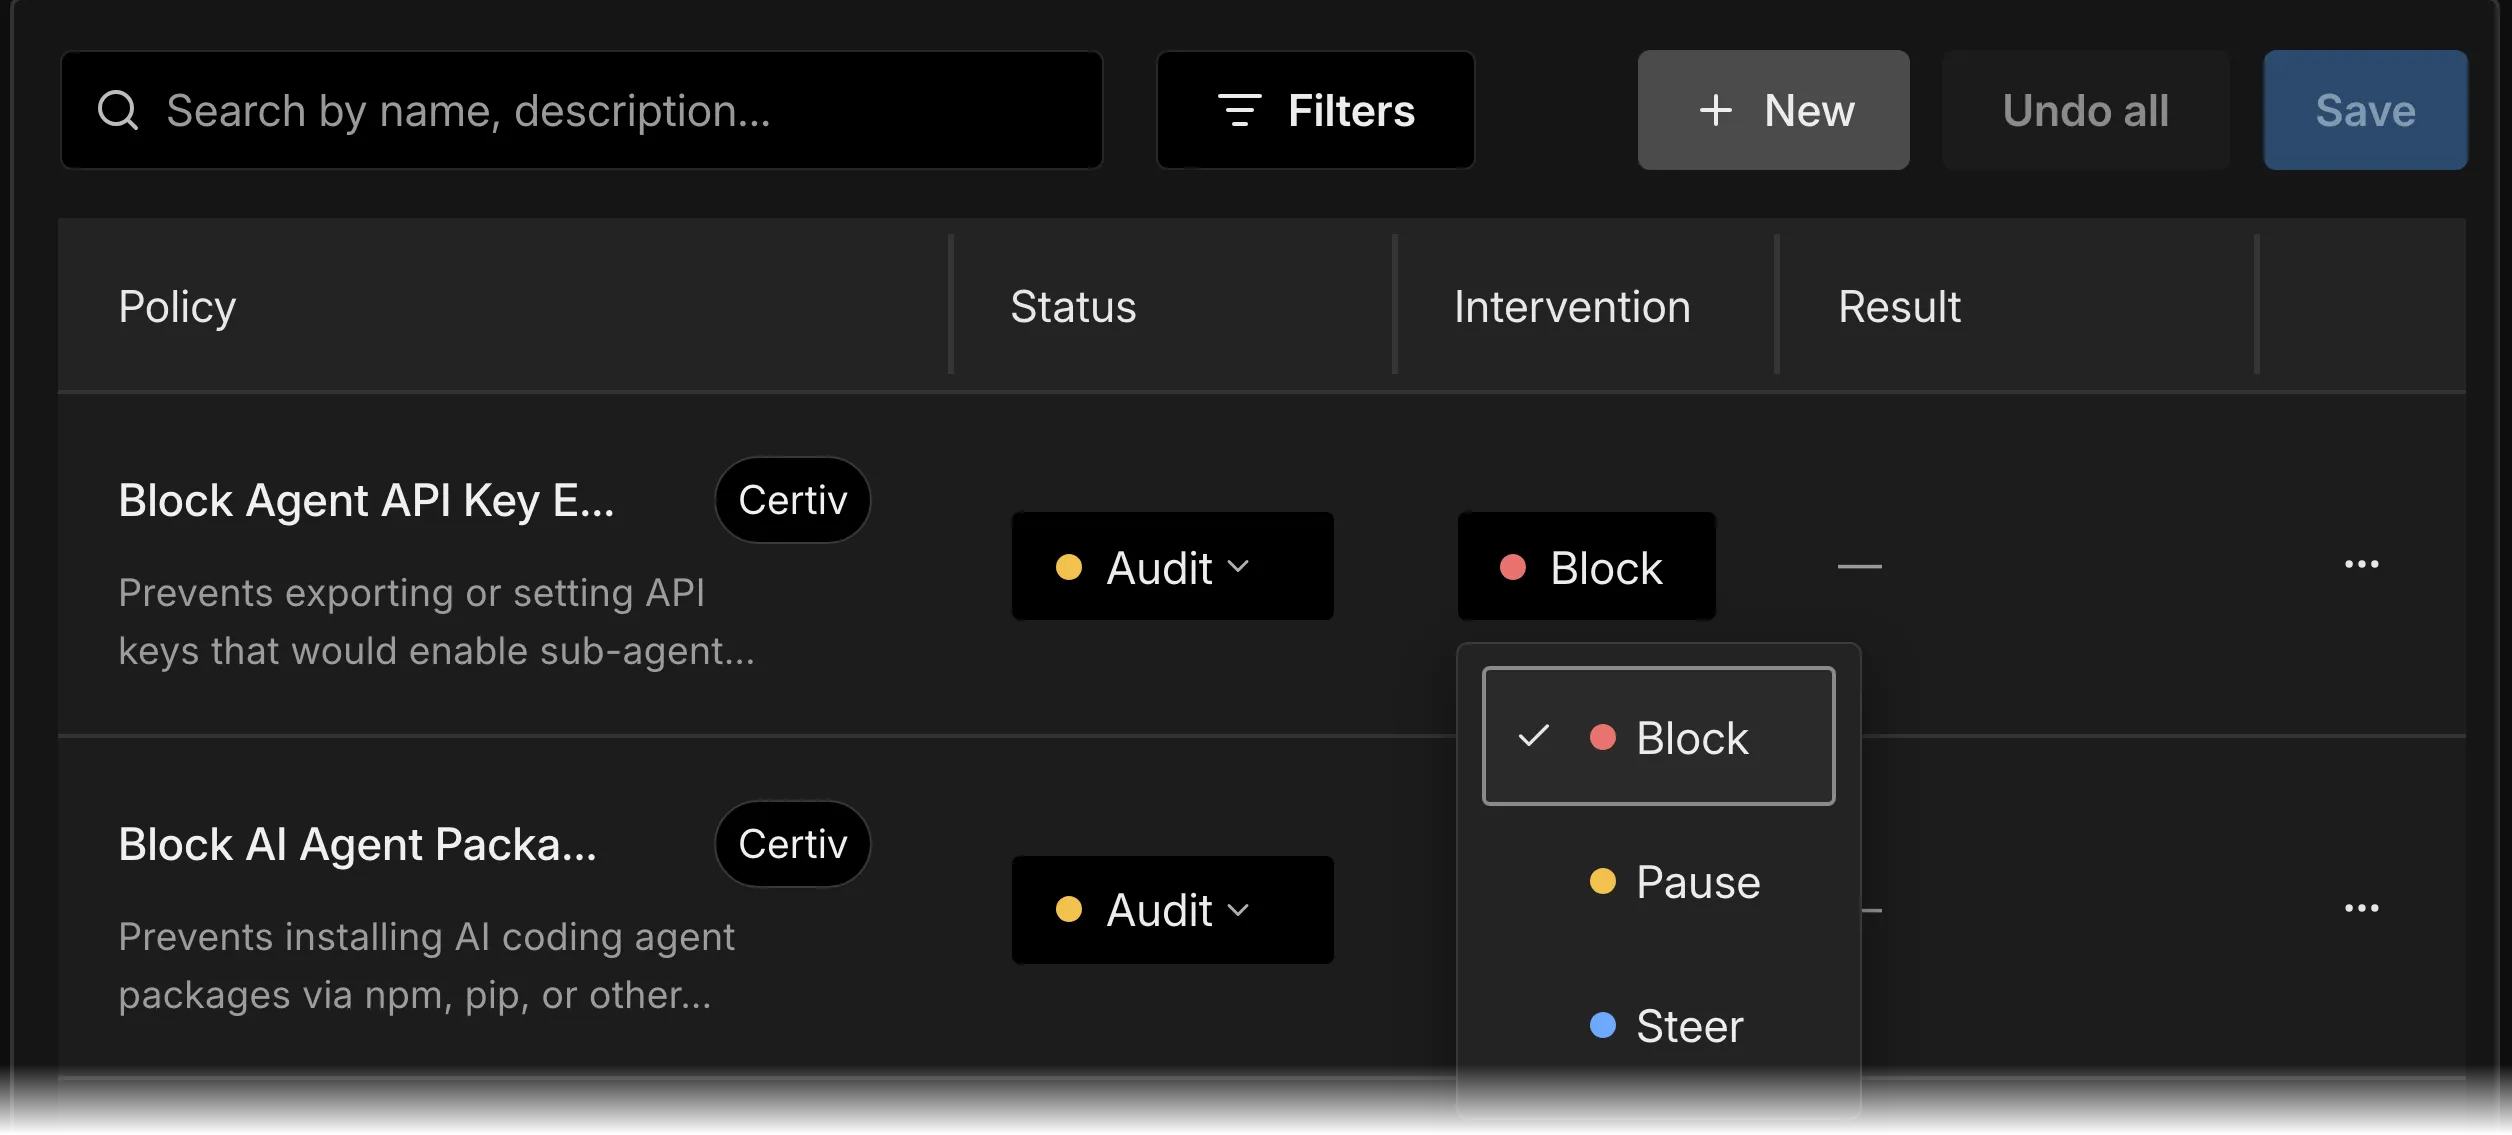
Scroll sideways to see the whole capture.
Product capture. Each policy has a status, such as Audit, and an intervention: Block, Pause, or Steer.
- One company policy One company policy applies to each supported agent and model.
- Managed policies → Policies Certiv maintains, enrolled for each group of agents as off, audit, or enforce.
- Custom policies Write your own, including rules described in plain language and judged by a model.
- Combined conditions A rule can combine several conditions.
- Policy tester Replays a recorded session against draft policies before they go live.
- Groups, overrides, and limits Enroll each group on its own, override a rule for one group, dry-run a change, and cap how often a rule fires.
- Model rules Allows or blocks the requested model against your model policy before the request goes out.
- Personal policies Rules a developer writes for their own device.
- Spend budgets Warn or enforce a spend limit for each endpoint.
Data Protection
Keep secrets out of what agents send.
Certiv removes matched credentials from an agent request before it is sent, and blocks tool calls that send secrets or source code to a remote host.
- Secret redaction → Removes matched API keys, access tokens, and private keys from agent requests that can be rewritten, before they are sent.
- Credential access Blocks reads of .env files, SSH and cloud keys, and other credential stores.
- Exfiltration Blocks a tool call that sends secrets or proprietary source code to a remote host.
- Permanent deletion Blocks irreversible deletes such as rm -rf, force pushes, and DROP TABLE.
Audit and Evidence
See what each agent did, and why.
Policy decisions are kept with the policies considered, the outcome, and the reasoning, and each session reads as a timeline.
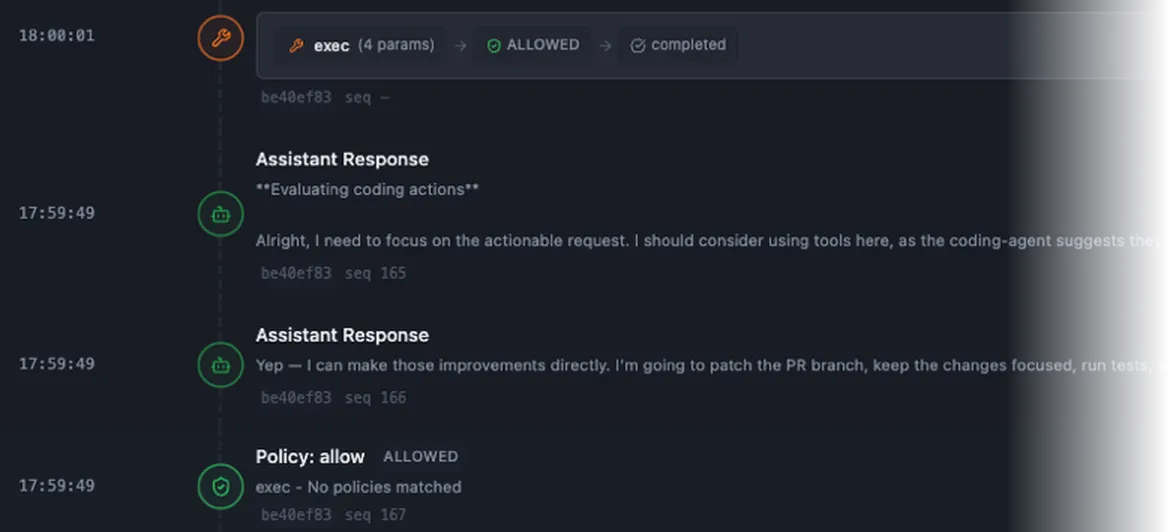
Scroll sideways to see the whole capture.
Product capture. A session log in time order: the agent’s responses, a tool call, and the policy decision that allowed it.
- Session timeline → Each agent session step by step, with a summary, a context graph, and export.
- Decision log Each policy decision, with the policies considered, the outcome, and the reasoning. Export the event list as PDF or CSV.
- Audit mode A policy records what it would do without enforcing, so you can watch before you enforce.
- Framework mapping → Each managed policy maps to entries in OWASP, MITRE ATT&CK, and NIST AI RMF.
- Dashboards Top models, policy frequency, token usage, and the most active agents.
- Usage and spend Spend for each session, endpoint, user, and model, at your contract rates.
- Signed decision receipts Each decision signed with Ed25519.
- Privacy Mode Keeps compliant sessions private. Viewing one needs a reason, shown to the developer, and lasts 24 hours.
Deploy and Operate
Install Scout once. Run it on the fleet.
Scout deploys through the device-management tools your IT team already runs, including Iru, Jamf Pro, and Microsoft Intune. It reports its health and updates remotely on macOS and Windows.
State
- Enabled 105
- Disabled 35
Scout version
- 1.3.0 118
- 1.2.4 22
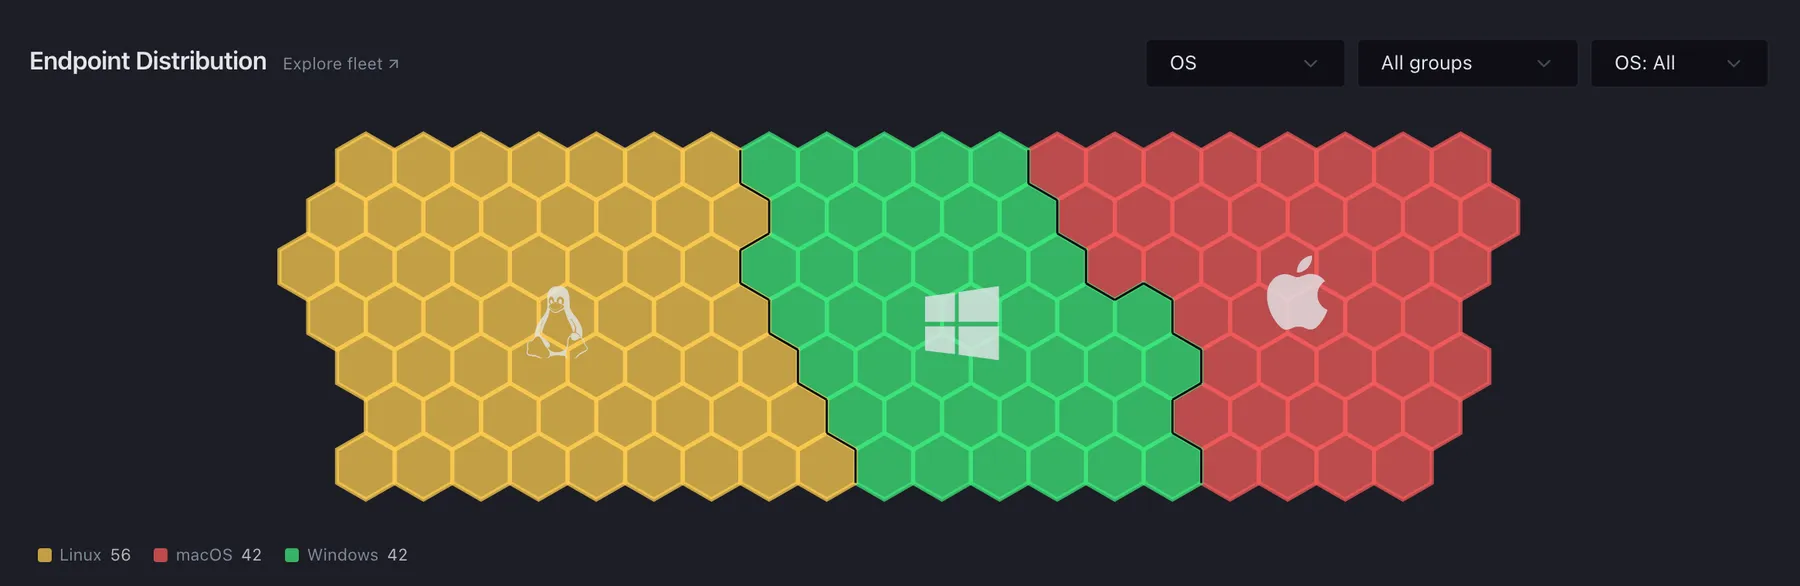
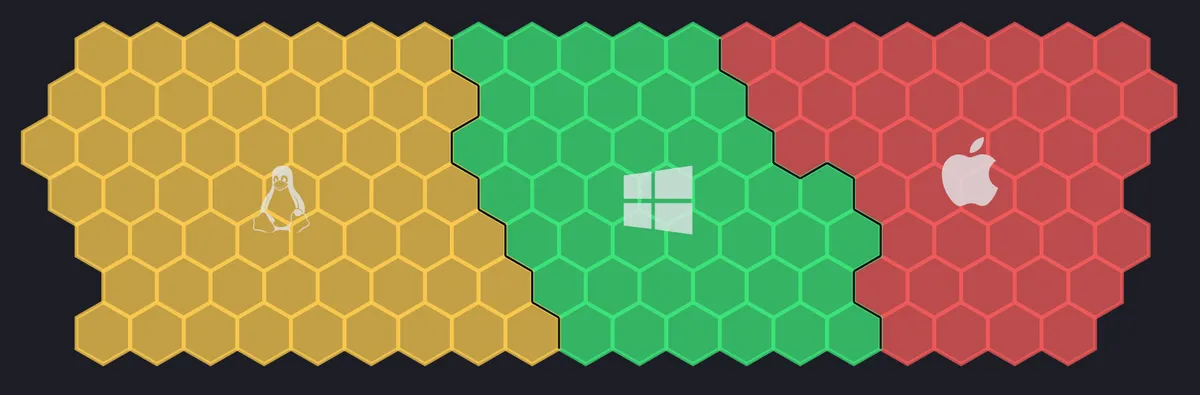
Product capture and demo data. A demo fleet of 140 endpoints: 56 on Linux, 42 on Windows, and 42 on macOS. The State and Scout version panels color the same 140 endpoints by those two per-endpoint columns in the console.
- macOS, Windows, and Linux → macOS 15 and later, Windows 10 and 11, and Linux .deb and .rpm packages.
- Device-management deployment Deploys through the tools your IT team runs, including Iru (Kandji), Jamf Pro, and Microsoft Intune, and with SCCM and Group Policy.
- Console fleet view → Endpoints with their agents, in one console.
- TLS inspection control Turn inspection off for the whole organization, or add exceptions.
- Health and updates Scout reports its health, and updates remotely on macOS and Windows.
- Single sign-on and MFA Sign in with Google or your enterprise identity provider, and require MFA.
- Time-boxed Support access Give Certiv Support access for a limited time.
- The certiv command line Decisions, pauses, and enforcement results from the command line on the endpoint.
- Integrations Webhook, CrowdStrike NGSIEM, Slack, and Google Cloud DLP.
Discover, decide, and prove, in one product.
One product covers the whole path, from the first agent found on a device to each decision and its record. Book a demo to see it on your own agents.